Discovery
AI reads the paths that crawlers walk past
It reads screens like a person and maps paths, parameters, and multi-step input flows.
Every later stage builds on this context.
- Page and screen context analysis
- Multi-step forms and input flows
Built on the know-how of elite hackers, our AI hacks your service for real.It doesn't stop at a list of vulnerabilities. From chaining attacks to reproducing them, it all unfolds in real time.
Attackers use AI to find vulnerabilities, then let it run from intrusion to exfiltration on its own.They no longer need skilled people or long preparation.
80–90%
AI carried out most of the attack itself.In a campaign against about 30 organizations, humans stepped in only 4–6 times.
Source: Nov 2025 · Anthropic threat report
600+
A low-skilled attacker used commercial AI to take over 600+ security devices in 55 countries.AI drew up the attack plans and built the tools.
Source: Feb 2026 · Amazon Threat Intelligence
5M runs
AI found a 16-year-old flaw that automated tests had missed across 5 million runs.In an attacker's hands, it finds them just as fast.
Source: 2026 · Anthropic Project Glasswing
Every stage builds on the same context, and every request must pass the guardrails before it goes out.You can watch the whole process in real time.
AI reads the paths that crawlers walk past
It reads screens like a person and maps paths, parameters, and multi-step input flows.
Every later stage builds on this context.
Where other DAST tools stop at the login, we start
Authentication that's hard to automate, like SSO, MFA, and digital certificates, goes through a human in the loop.
The AI takes over the authenticated session and scans the screens behind the login.
No blind flooding.It reads the context and aims precisely
Instead of brute-forcing payloads, it designs scenarios that fit the screen context and your industry's business logic.
Every request must pass the guardrails before it goes out.
See what the AI sees, as it sees it
The screen under scan and the attack log unfold in real time.
See what went out and what was blocked, even while your service is live.
We filter out the uncertain and report only what's proven
Follow-up exploits confirm it can really be breached and how far the damage could spread.
How it was detected and the request/response packets are kept as evidence.
Checking the fix takes one click
It replays the exact same attack to confirm the fix.
Results build up run by run and serve directly as audit evidence.
Manage AI scans, retests, and history on one platform.Records build up per asset and per run, so changes in your security posture are clear at a glance.

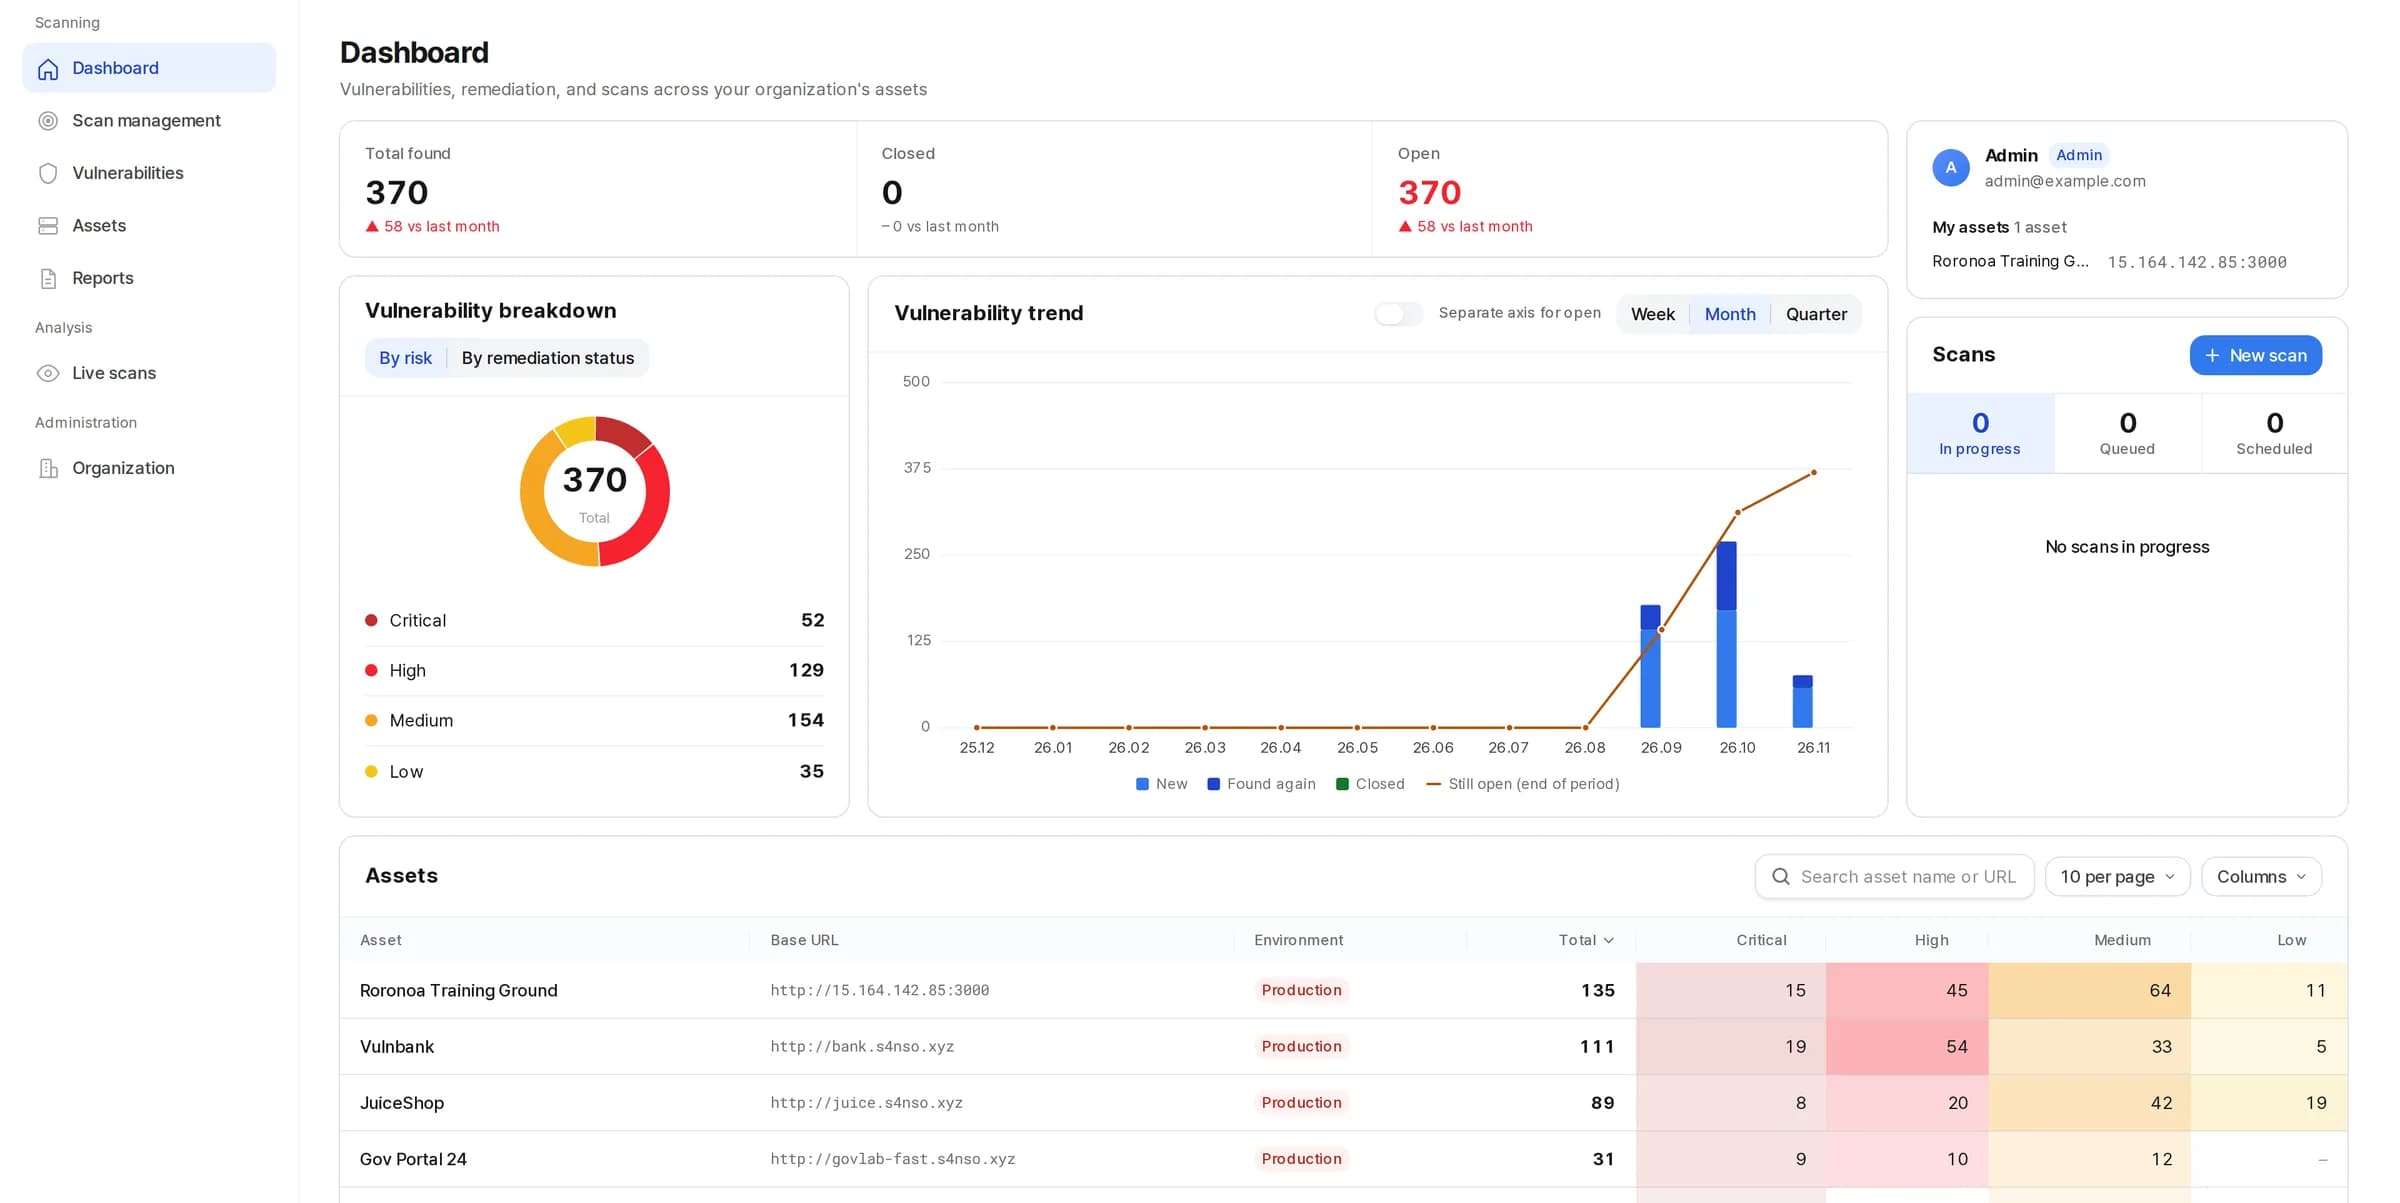
From scans in progress to vulnerability stats, remediation status, and trends by run.See the security posture of your web assets on one screen.
Group vulnerabilities by risk and type.One list keeps the full history, from discovery through retest to fix.
Reports by run, asset, or vulnerability are generated instantly.From the cover to details and recommended fixes, they're ready to submit as is.
Three roles, two-factor authentication, and IP access policies control access.Audit logs track every action and who is accountable.
Rule-based DAST is fast but stalls at logins and result verification.Manual pen testing goes deep but takes two days per web service.OFFen AI DAST takes the strengths of both: AI designs the attacks and proves them with exploits.
6–9hrs
To scan one web service.Manual testing takes about two days.
85% less
Scanning effort saved by automating discovery, payloads, and verification.
2×
More true positives than typical DAST.True positive rate, OWASP Benchmark.
Half
The false positives of typical DAST.False positive rate, OWASP Benchmark.
※ In-house test results
Authenticated areas
Login · multi-step forms
Detection
How issues are judged
Result verification
Who filters false positives
Safety
Side effects on live services
Request traffic
Requests per scan
Time required
One web service
Scan records
Evidence left behind
* In-house test results
Results are classified by each framework's check items.Use them as is in vulnerability assessment reports and retests.
Public sector · infrastructure
Sorts results by the web items in the vulnerability assessment guide.
Finance
Turns web and API scan results for e-finance services into evidence reports.
International standard
Maps findings to OWASP Top 10 items.
A record of researching attacks ourselves, with the security certifications and awards for how we manage the results.
ISO/IEC 27017
Information security in cloud services
ISO/IEC 27001
Information security management system
ISO 9001
Quality management system
GS certification
Software quality · OFFen v1.0
Invention compensation
Certified excellent company
Inno-Biz AA
Technology-innovative SME
Excellent tech T-3
Penetration testing · threat intelligence · vulnerability research
Choose a SaaS subscription, an Appliance, or a managed service.
Cloud subscription, ready to use
Cloud
Start right away, no installation.
AI-assisted pen testing, outsourced
Outsourced
Pen-testing experts and the AI Hacker deliver a tailored service.
Server installed on your internal network
On-prem
Fits air-gapped environments too.
Yes. Every request must pass guardrail checks before it's sent, and risky actions like spam posts or account creation are blocked.A scan sends under 8,000 requests, and we agree on scan windows and WAF/IP exceptions in advance.
Yes. Sign in live in the browser that opens before the scan, and the AI uses that session to scan the screens behind the login.Authentication that's hard to automate, like SSO, OTP, and digital certificates, works the same way.
It depends on the size of the asset, but a scan takes 6–9 hours on average.
It depends on the deployment option.SaaS and Managed are priced by the number of assets and scans, and Appliance by the size of the servers delivered.For a detailed quote, .
AI is used for endpoint discovery, vulnerability scanning, report generation, and retesting.